
Uncovering the Security Breach in the FlyDubai Hijacking Incident
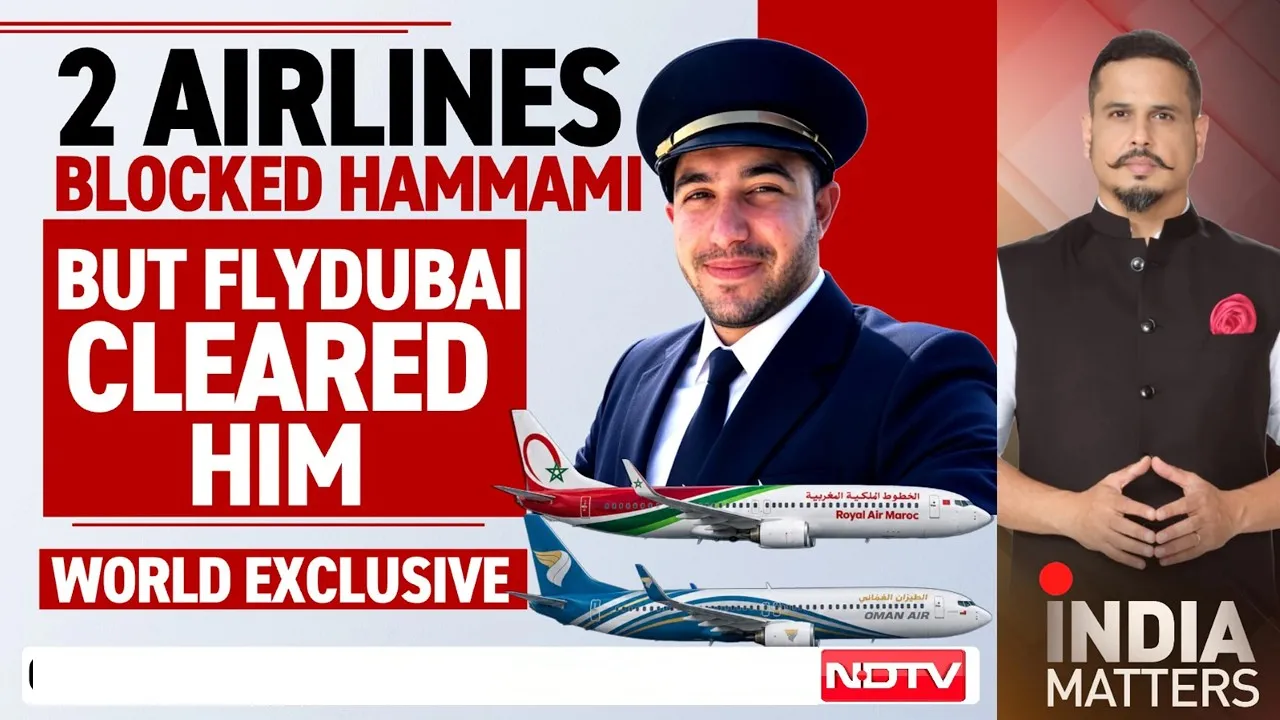
The recent investigation surrounding the FlyDubai hijacking incident involving Hamam Al Hammami has unveiled a troubling narrative that extends beyond the cockpit events to significant lapses in aviation security protocols. Al Hammami, who was grounded in Oman and subsequently rejected by Royal Air Maroc, ultimately secured a position with FlyDubai. This series of events has raised critical questions regarding the effectiveness of communication and information sharing among aviation regulators, airlines, and security agencies. As the inquiry expands, it becomes evident that there are unanswered questions regarding the adequacy of the measures in place to prevent individuals like Al Hammami from accessing sensitive areas of airport operations.
The scrutiny of Al Hammami's journey through multiple layers of aviation security highlights the pressing need for a comprehensive examination of the processes that enable or hinder potential threats. Did regulatory bodies effectively communicate his history or concerns that could have prevented his hiring? What protocols were overlooked that allowed him to slip through the cracks? These inquiries are not merely academic; they hold significant implications for the future of aviation safety and security, especially in light of the recent hijacking incident that has sent shockwaves through the industry.
As investigators delve deeper, it is crucial to understand whether there were missed opportunities to intercept Al Hammami before he ever entered the cockpit of a FlyDubai aircraft. This incident serves as a stark reminder of the vulnerabilities within the aviation system and the imperative for enhanced security measures that can effectively safeguard against potential threats.
As reported by youtube.com.